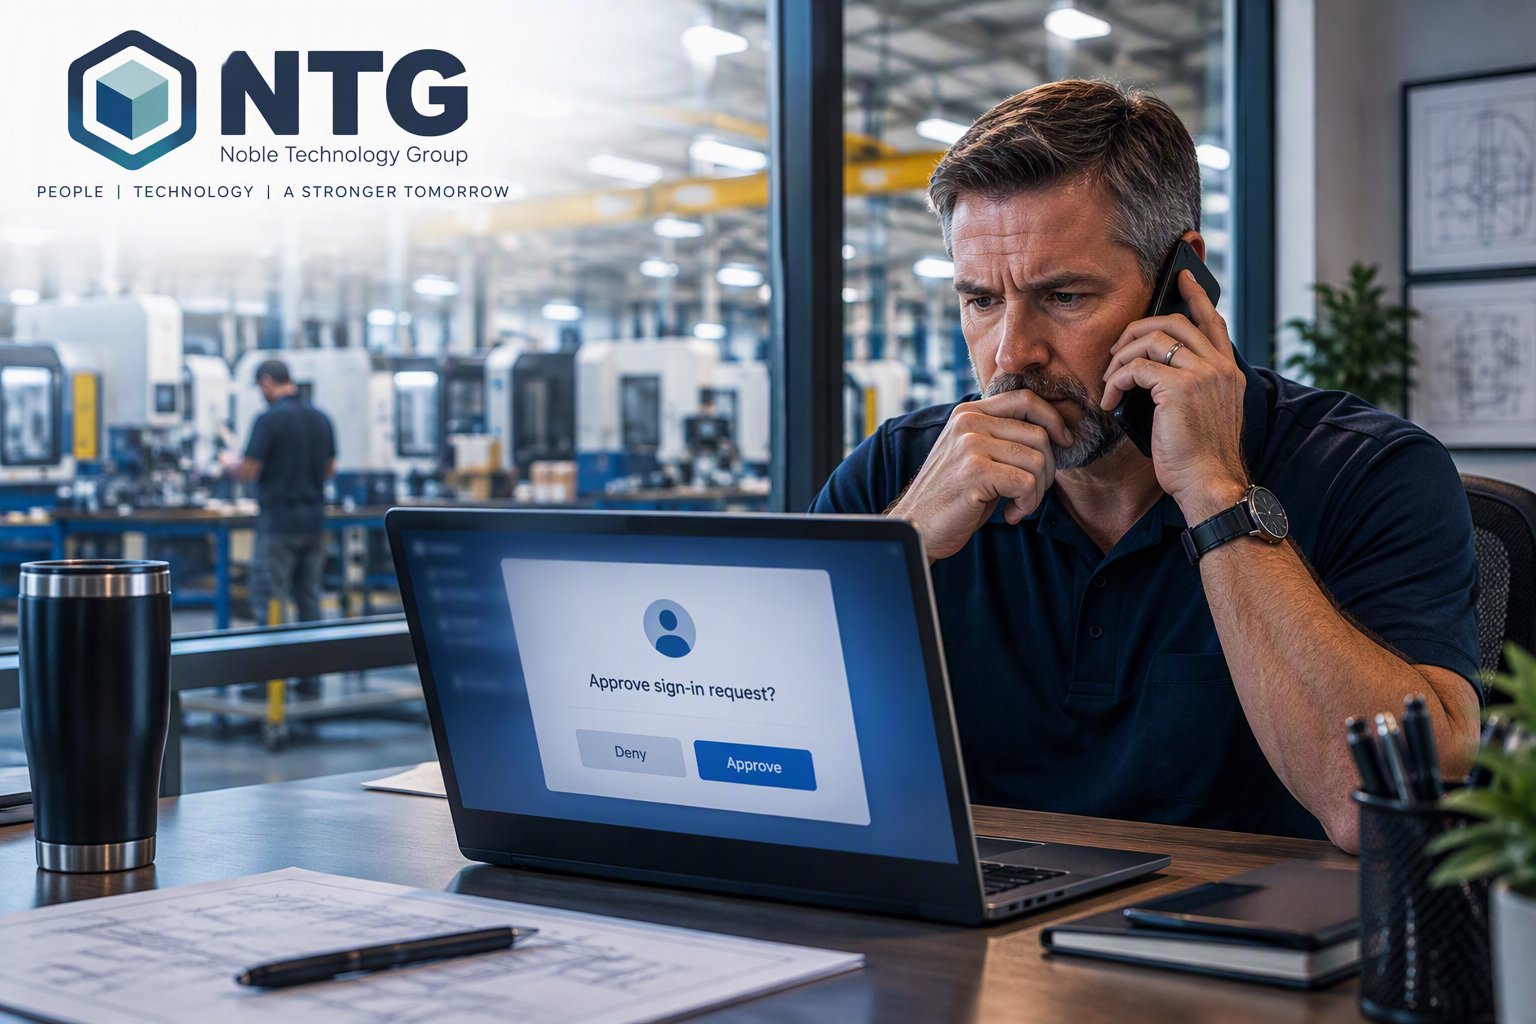
Microsoft 365 phishing attacks often begin with convincing phone calls that trick employees into approving unauthorized access requests.
By Peter Noble, Founder and CEO of Noble Technology Grou
One of your employees receives a call from IT.
At least, that’s what they think.
The caller knows enough about the company to sound credible. They explain that Microsoft 365 security is being updated and ask the employee to approve a new authentication method.
The request sounds legitimate, and that is exactly what makes it dangerous.
The employee follows the instructions, completes multifactor authentication, and returns to work. Nothing crashes. No warning appears.
Meanwhile, an attacker may have gained access to the company’s Microsoft 365 environment.
Key Takeaway: The attacker does not always have to break your security. Sometimes, they convince an employee to open the door.
You do not need to become a Microsoft security engineer to reduce this risk. You need a clear process, a prepared team, and an IT partner who can help you find and close the gaps.
In This Article
- Why This Matters to Your Business
- How the Microsoft 365 Phishing Attack Works
- Could Your Company Stop This Attack?
- What Should You Ask Your IT Provider?
- Frequently Asked Questions
Why This Matters to Your Business
Microsoft 365 is no longer just an email system.
Depending on how your company uses it, the platform may contain or provide access to:
- Customer and vendor communications
- Quotes and purchase orders
- Production schedules
- Contracts and pricing
- Employee and financial information
- Engineering documents
- Compliance policies and evidence
The potential exposure depends on what the compromised employee is authorized to access.
For an operations manager, this is not simply an IT problem. It can quickly become a customer, production, financial, compliance, or business continuity problem.
How the Microsoft 365 Phishing Attack Works
Like many successful cyberattacks, this one relies less on brilliant technology and more on human trust.
1. The Attacker Researches the Company
Attackers gather information about employees and organizational structures from public sources, including company websites, LinkedIn profiles, social media, and other publicly available information.
They do not need your entire organizational chart. They need just enough information to sound like they belong in the conversation.
2. Fake IT Support Contacts an Employee
The attacker may call or message an employee and claim that a passkey, MFA method, or sign-in setting must be updated immediately.
Attackers understand that urgency can short-circuit good judgment. The faster they can get someone moving, the less likely that person is to stop and verify the request.
3. The Employee Authorizes Access
The employee may be directed to a website that resembles a Microsoft sign-in page.
In other cases, the employee may be sent to a legitimate Microsoft sign-in page and instructed to enter a code supplied by the attacker.
That means seeing a real Microsoft page is not enough. The employee must also verify who initiated the request and what is being authorized.
4. The Attacker Attempts to Stay Inside
Once access is gained, attackers often try to establish persistence by adding authentication methods under their control and exploring what information is available to the compromised account.
This is why changing a password alone is not always enough after an account compromise.
Could Your Company Stop This Attack?
Give yourself one point for every question you can answer with a confident "yes."
- Would employees verify an unexpected request from IT?
- Does everyone know the correct IT support channel?
- Would your provider detect an unfamiliar authentication method?
- Can suspicious Microsoft 365 sessions be investigated and contained?
- Does leadership know who takes charge after an account compromise?
If you scored fewer than four points, that does not automatically mean your environment is insecure.
It means your process deserves a closer look.
Give Employees a Four-Step Plan
Employees should not have to make complicated cybersecurity decisions during an unexpected phone call.
1. Stop
Do not approve an unexpected request simply because the caller sounds convincing.
2. Verify
Contact your regular IT support team using a known phone number, email address, or support portal. Never use the contact information supplied by the caller.
3. Report
Report the request even if no information was entered. The attacker may be contacting other employees.
4. Speak Up Quickly
If an employee clicked a link, entered a code, or approved the request, they should report it immediately.
Fast reporting matters more than avoiding embarrassment. I would rather receive an uncomfortable phone call two minutes after the click than a beautifully written explanation two weeks later.
What Should You Ask Your IT Provider?
You do not need to manage Microsoft 365 security yourself. You do need to know who is accountable for it.
Ask your provider:
- Do we use phishing-resistant MFA where appropriate?
- Are Conditional Access policies configured?
- Can unmanaged devices access company information?
- Who reviews newly registered authentication methods?
- Can unusual SharePoint or OneDrive activity be identified?
- Do we have a documented incident response plan?
- When did we last test that plan?
If you do not receive clear answers, you may have uncovered an important gap.
Where Compliance and Cyber Insurance Fit
Depending on the insurer and policy, a compromised Microsoft 365 account may raise questions about the security controls represented in your cyber insurance application.
Your documented answers should match the controls you actually maintain.
For defense contractors, Microsoft 365 may also be relevant to CMMC and NIST SP 800-171 compliance efforts when it stores, processes, or transmits covered information.
A written policy is useful, but it must match what your company actually does. Otherwise, it is just office décor with bullet points.
Your Job Is to Keep the Business Moving
Your goal is not to guarantee that nobody will ever click the wrong link.
Your goal is to create layers of protection so one mistake does not become a company-wide crisis.
A proactive managed IT services strategy can connect:
- Microsoft 365 administration
- Identity and access security
- Employee IT support
- Security monitoring
- Incident response
- IT consulting
- Compliance services
When comparing managed IT services in San Diego, look beyond password resets and computer repairs.
Choose a provider that can help you protect operations, support employees, manage cloud security, and prepare for security incidents.
At the end of the day, your job is not to become a cybersecurity expert.
Your job is to keep the business running, protect your employees, serve your customers, and reduce unnecessary risk.
A good IT partner helps you do exactly that.
Responsive IT Support Makes the Plan Work
Technology helps prevent attacks. Trust helps contain them.
When employees feel comfortable reporting a mistake immediately, your company has a much better chance of limiting the damage.
"Professional, quick to respond, and highly knowledgeable."
That is how one Noble Technology Group client described our team.
Another client praised our "fast, knowledgeable solutions" and highlighted the calm, patient assistance received after clicking something they should not have clicked.
That is the kind of relationship employees should have with IT. People should feel comfortable speaking up quickly, especially when something does not feel right.
Frequently Asked Questions
Can multifactor authentication stop Microsoft 365 phishing attacks?
MFA remains one of the most important security controls available. However, some phishing attacks attempt to trick users into approving an attacker’s request. Stronger protections such as phishing-resistant MFA and employee verification procedures can further reduce risk.
How do attackers gain access to Microsoft 365 accounts?
Attackers commonly use social engineering, impersonation, phishingnvince users to authorize access.
Should businesses monitor authentication changes?
Yes. New authentication methods or unexpected account changes can be indicators of compromise and should be reviewed promptly.
Is changing the password enough after an attack?
Not always. Security teams may also need to investigate active sessions, remove unauthorized authentication methods, and review cloud activity.
Can managed IT services help secure Microsoft 365?
A managed IT services provider can help coordinate Microsoft 365 administration, identity security, employee support, monitoring, incident response, and compliance requirements.
How Confident Are You in Your Microsoft 365 Security?
If an employee received this call tomorrow, would your team know exactly what to do?
If you're not completely sure, now is the right time to find out.
At Noble Technology Group, we help business leaders identify gaps in:
- Microsoft 365 security
- Employee verification procedures
- Cloud access controls
- Compliance responsibilities
- Incident response planning
The goal is not to create fear.
The goal is to give you confidence.
Let's identify the gaps before an attacker does.