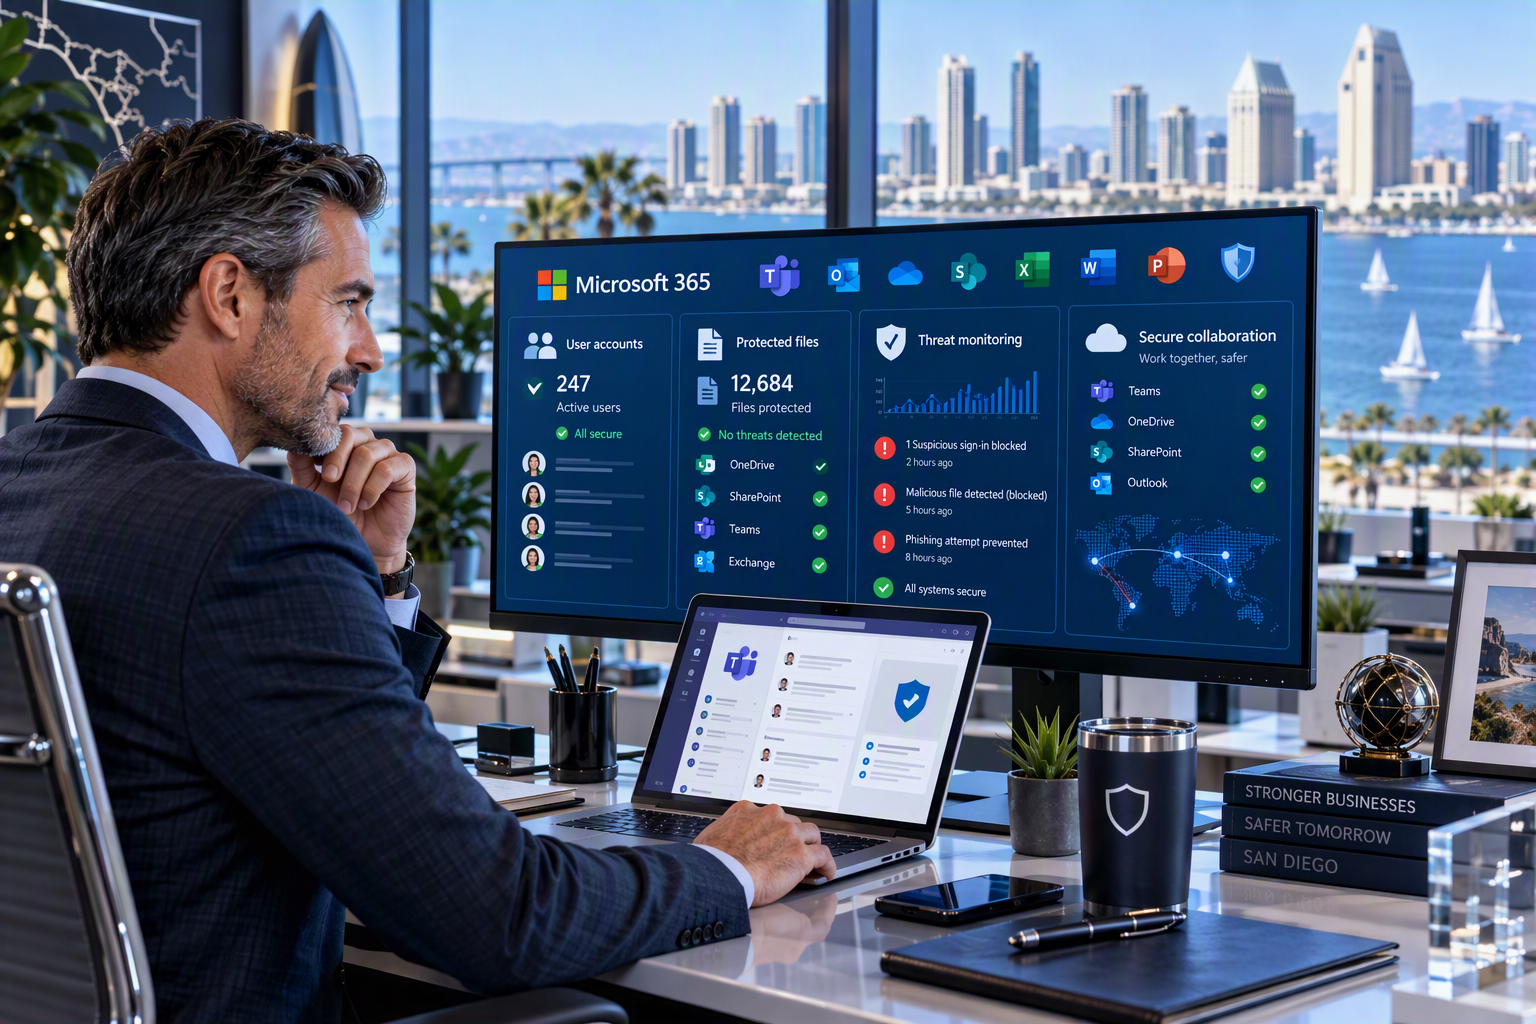
As cybercriminals increasingly target collaboration platforms, businesses should review Microsoft Teams and Microsoft 365 security controls to reduce risk and support cyber insurance requirements.
Microsoft Teams Security Risks for San Diego Businesses
By Peter Noble, Founder & CEO, Noble Technology Group
Your company has probably spent years strengthening email security.
You’ve invested in spam filtering, multifactor authentication, employee training, and cybersecurity tools designed to keep threats out of your inbox.
Unfortunately, cybercriminals have adapted.
Today, many security risks don’t arrive through email at all. They arrive through the collaboration platforms your employees use every day.
Across San Diego County, businesses rely on Microsoft Teams for communication, remote work, project collaboration, customer service, and daily operations. From manufacturers and professional services firms to healthcare organizations and defense contractors, Teams has become an essential business platform.
That’s great for productivity. It’s also why attackers are paying attention.
As organizations become better at identifying suspicious emails, cybercriminals are targeting collaboration platforms where employees may be more trusting and less cautious.
If you’re responsible for protecting customer data, maintaining compliance, satisfying cyber insurance requirements, or keeping your business running smoothly, understanding Microsoft Teams security risks is no longer optional.
It’s part of protecting your business.
Quick Answer: Are Microsoft Teams Security Risks Real?
Yes. Microsoft Teams security risks include phishing attacks delivered through chat, malware hidden in shared files, compromised user accounts, unauthorized guest access, credential theft, and accidental exposure of sensitive business information.
Businesses can reduce these risks through multifactor authentication, employee security awareness training, Microsoft 365 security controls, endpoint protection, and proactive managed IT services.
The companies most vulnerable to cyberattacks aren’t necessarily using the wrong technology. They’re often relying on the wrong assumptions about what’s safe.
The Hidden Microsoft Teams Risk Most Businesses Aren’t Thinking About
Most employees have been trained to approach email with caution.
They know phishing attacks exist. They know suspicious links can be dangerous. They know not every attachment should be trusted.
Microsoft Teams feels different.
Messages often come from coworkers, customers, vendors, suppliers, and business partners your employees already know. Communication happens quickly and feels less formal than email.
As a result, people naturally lower their guard.
Cybercriminals understand this behavior. They know an employee may be more likely to trust a file that appears to come from a familiar colleague than an unexpected email from an unknown address.
The problem isn’t Microsoft Teams itself. The problem is misplaced trust.
Cybercriminals don’t attack technology first. They exploit trust.
Why Microsoft Teams Security Matters for San Diego Businesses
Companies throughout San Diego County face a wide range of cybersecurity and compliance challenges.
Many local organizations operate in regulated, security-sensitive, or operationally demanding industries, including:
- Manufacturing
- Aerospace
- Defense contracting
- Healthcare
- Financial services
- Professional services
- Engineering and construction
For these businesses, a cybersecurity incident can create consequences that extend far beyond the IT department.
A compromised Microsoft Teams or Microsoft 365 account could expose:
- Customer information
- Financial records
- Engineering drawings
- Intellectual property
- Contracts and project documents
- Employee information
- Controlled Unclassified Information
Organizations working toward CMMC, NIST SP 800-171, HIPAA, DFARS, or other industry requirements must recognize that communication and collaboration platforms are part of the larger security environment.
Teams, SharePoint, OneDrive, employee devices, access controls, and business processes must work together to protect sensitive information.
What’s Really at Risk?
When people hear the phrase “cybersecurity incident,” they often think about ransomware, malware, or hackers.
But that’s not what you’re really trying to protect.
You’re protecting:
- Your ability to serve customers
- Your employees’ productivity
- Your company’s reputation
- Your customer and vendor relationships
- Your revenue and profitability
- Your compliance obligations
- Your future growth opportunities
A successful attack can disrupt operations almost immediately. Employees may lose access to files, projects may stop moving forward, customers may experience delays, and leadership may be pulled into emergency response instead of running the company.
Cybersecurity isn’t just about preventing malware. It’s about protecting everything you’ve worked hard to build.
How Microsoft Teams Attacks Can Happen
Many business leaders assume cyberattacks require highly sophisticated hacking techniques.
In reality, an incident can begin with one familiar-looking message and one understandable mistake.
1. A trusted account is compromised
An attacker gains access to a vendor’s, customer’s, or employee’s Microsoft 365 account through phishing, credential theft, a reused password, or another form of account compromise.
2. A Teams message is sent
The attacker uses the compromised account to send a message, link, or file through Microsoft Teams.
3. An employee trusts the sender
The sender appears familiar. The conversation may even seem to fit the employee’s normal work, so the employee has little reason to suspect a problem.
4. The link or file is opened
The attachment may contain malicious content, or the link may direct the employee to a fraudulent Microsoft 365 sign-in page designed to steal credentials.
5. The attack expands
Once credentials or device access are obtained, the attacker may attempt to access additional accounts, applications, files, customers, vendors, or financial systems.
The initial action may take less than a minute. The resulting business disruption can last much longer.
This is why a modern cybersecurity strategy must extend beyond email protection.
Microsoft’s Teams File Protections Help, but They Aren’t Enough
Microsoft has been expanding protections designed to reduce the danger associated with risky files shared through Teams.
These protections give administrators more control over the types of files employees can exchange. If your organization has no valid business reason to share a particular high-risk file type through Teams, blocking it can remove an unnecessary attack path.
That is a practical security improvement.
However, file blocking is only one layer of protection. It cannot compensate for weak passwords, incomplete multifactor authentication, excessive permissions, unprotected endpoints, limited employee training, or insufficient account monitoring.
No single Microsoft Teams setting can stop every threat.
Effective cybersecurity comes from multiple safeguards working together.
Microsoft Teams Security Best Practices
If you’re looking for practical steps your organization can take, begin with the fundamentals.
- Enable multifactor authentication: Require MFA for every user, especially administrators and people with access to sensitive systems.
- Review guest access: Confirm that vendors, contractors, former employees, and outside collaborators retain only the access they still need.
- Remove unused accounts: Inactive or abandoned accounts create unnecessary exposure.
- Block unnecessary file types: Restrict file formats that have no legitimate business purpose in your Teams environment.
- Protect employee devices: Use centrally managed endpoint security to detect and contain malicious activity.
- Secure administrator accounts: Administrative access should be tightly limited, protected, and monitored.
- Monitor account activity: Investigate unusual sign-ins, unexpected access patterns, and suspicious changes.
- Keep devices updated: Apply security patches to operating systems, browsers, applications, and business devices.
- Train employees: Teach your people to question unfamiliar files, unexpected requests, and unusual messages, even when they appear in Teams.
- Prepare for incidents: Create an incident response plan before you need it.
Microsoft Teams Security Checklist
- Multifactor authentication is enabled for all users
- Administrator accounts receive additional protection
- Guest and external access are reviewed regularly
- Inactive accounts are removed or disabled
- Unnecessary file types are restricted
- Endpoint protection is centrally managed
- Microsoft 365 activity is monitored
- Employees receive ongoing security awareness training
- Critical business data is backed up appropriately
- Cyber insurance requirements are reviewed before renewal
- A documented incident response plan is maintained
- Periodic cybersecurity assessments are completed
No single control eliminates risk. Together, however, these safeguards create a more resilient business.
Cyber Insurance Requirements Are Raising the Security Bar
Cyber insurance providers increasingly want evidence that businesses are taking reasonable steps to manage cybersecurity risk.
Applications and renewal questionnaires commonly examine areas such as:
- Multifactor authentication
- Endpoint detection and response
- Security awareness training
- Microsoft 365 security controls
- Access management
- Backup and disaster recovery
- Patch management
- Incident response planning
If your answers don’t accurately reflect your security environment, you may discover gaps during underwriting, renewal, or after an incident.
This is one reason I encourage business leaders to review cyber insurance requirements before the renewal deadline. Waiting until an application is due can turn a manageable security project into a rushed operational problem.
A stronger security posture can do more than support an insurance application. It can reduce the likelihood that your company ever needs to make a claim.
A Simple Three-Step Plan to Reduce Microsoft Teams Security Risks
Cybersecurity can feel complex, but your next steps don’t have to be.
Step 1: Identify your security gaps
Review the parts of Microsoft 365 that affect your people and sensitive information, including:
- Microsoft Teams settings
- SharePoint permissions
- OneDrive sharing policies
- User and administrator access
- Multifactor authentication coverage
- Guest accounts
- Endpoint security
- Monitoring and alerting
You can’t address risks you haven’t identified.
Step 2: Strengthen the highest-priority defenses
Focus first on weaknesses that could have the greatest operational or security impact. Depending on your environment, that may include MFA, administrative access, endpoint protection, employee training, file-sharing controls, backups, or security monitoring.
Step 3: Review and improve regularly
Cybersecurity isn’t a one-time project. Employees join and leave, vendors change, permissions accumulate, threats evolve, and Microsoft 365 capabilities continue to change.
Regular reviews help keep your security strategy aligned with your business.
The goal isn’t perfect security. The goal is reducing risk while helping your team do its best work.
Why Managed IT Services in San Diego Matter More Than Ever
Most business owners, operations managers, and executives aren’t Microsoft 365 security experts. They shouldn’t have to become one just to keep their organizations moving forward.
Your focus should remain on customers, employees, operations, and growth.
The challenge is that cybersecurity requires regular attention. New threats emerge, Microsoft 365 changes, compliance expectations evolve, and cyber insurance requirements become more demanding.
This is where experienced managed IT services in San Diego can create meaningful value.
The right IT partner can help you:
- Identify cybersecurity risks before they become incidents
- Strengthen Microsoft Teams and Microsoft 365 security
- Improve the reliability of your IT environment
- Support compliance initiatives
- Prepare for cyber insurance reviews
- Reduce avoidable operational disruption
- Create a practical technology roadmap
Good IT support shouldn’t create more complexity. It should give you a clear plan, reliable systems, and confidence that someone is paying attention to the risks your company cannot afford to ignore.
Common Microsoft 365 Security Challenges We See in San Diego
At Noble Technology Group, we work with organizations throughout San Diego County that are serious about protecting their operations but aren’t always sure where their greatest risks exist.
Common challenges include:
- Inconsistent multifactor authentication
- Excessive Microsoft Teams permissions
- Guest access that hasn’t been reviewed recently
- Limited visibility into Microsoft 365 activity
- Aging or inconsistently managed endpoint protection
- Cyber insurance questionnaire concerns
- Compliance readiness gaps
- Limited employee cybersecurity training
Many businesses already own at least some of the security technology they need.
The harder part is configuring it correctly, monitoring it consistently, documenting the controls, and improving the environment as the business changes.
That is where proactive IT consulting, compliance services, cybersecurity services, and managed IT services can make a measurable difference.
Make Secure Collaboration a Business Advantage
Microsoft Teams has changed how businesses communicate and collaborate. That isn’t going away.
The question isn’t whether your organization should use Microsoft Teams. The question is whether your organization is using it securely.
When cybersecurity is approached strategically, your employees can collaborate more confidently. Your company can be better prepared for compliance and cyber insurance reviews. Your leadership team gains greater visibility into risk. Your operations become more resilient.
The successful businesses of the future won’t be the ones that eliminate every possible risk.
They’ll be the ones that understand their risks, prioritize the right improvements, and keep strengthening their defenses without preventing people from doing their jobs.
That’s what modern cybersecurity is really about.
Not fear. Not unnecessary complexity. Business resilience.
Frequently Asked Questions About Microsoft Teams Security
Is Microsoft Teams secure for businesses?
Microsoft Teams includes numerous security and administrative controls. However, businesses must configure, monitor, and manage their broader Microsoft 365 environments appropriately. Security also depends on identity protection, employee devices, permissions, employee awareness, and ongoing oversight.
Can attackers use Microsoft Teams to deliver malware?
Attackers may use compromised accounts, malicious links, fraudulent sign-in pages, or dangerous files to target people through collaboration platforms. Employees should verify unexpected requests even when a message appears to come from a familiar contact.
Do cyber insurance requirements include Microsoft 365 security?
Cyber insurance questionnaires may ask about controls that directly affect Microsoft 365 risk, including MFA, access management, endpoint protection, security awareness training, backups, and incident response planning. Businesses should confirm the specific requirements of their policy and application.
Should small and midsize businesses worry about Microsoft Teams security?
Yes. Any business using Teams to exchange files, communicate with outside parties, or access sensitive information should include the platform in its cybersecurity planning.
How can San Diego businesses improve Microsoft Teams security?
Start by reviewing multifactor authentication, guest access, user permissions, file sharing, administrator accounts, endpoint protection, employee training, monitoring, backups, and incident response readiness. A Microsoft 365 security assessment can help prioritize the improvements that matter most.
Ready to Find Out Where Your Risks Are?
You shouldn’t have to guess whether your Microsoft 365 environment is secure.
Noble Technology Group helps businesses throughout San Diego strengthen Microsoft 365 security, improve compliance readiness, address cyber insurance requirements, and reduce cybersecurity risk through proactive managed IT services, IT support, IT consulting, cybersecurity services, and compliance services.
Whether you’re a manufacturer, healthcare provider, professional services firm, nonprofit, engineering company, or defense contractor, we can help you identify your risks and build a practical roadmap for improvement.